 TARUTICS
Web & API Security Assessment
A findings and remediation report format for authorized web and API assessments.
What needed solving
Owners need findings explained clearly and prioritized, not a raw list of technical output.
Built for: security teams, IT managers and business owners who need clear visibility and evidence-based findings.
What we built
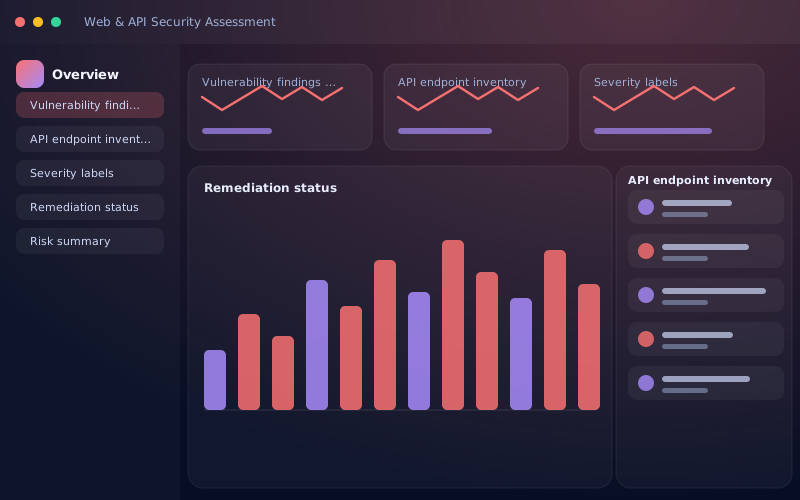
A structured report view with an endpoint inventory, severity labels, remediation status and a risk summary.
What is inside
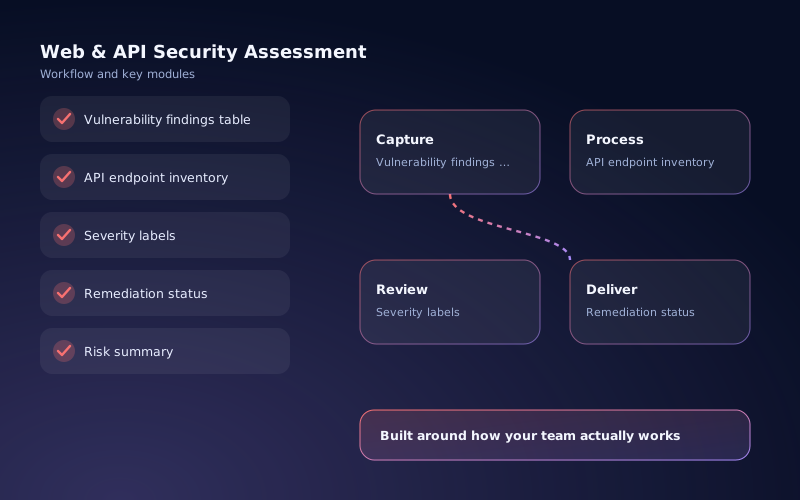
- ✓Vulnerability findings table
- ✓API endpoint inventory
- ✓Severity labels
- ✓Remediation status
- ✓Risk summary
A look at the product
Click an image to enlarge it.
From idea to launch
- 1
Understand
We map how security teams, IT managers and business owners work today and what vulnerability findings table has to achieve.
- 2
Design
Wireframes and a clickable layout for vulnerability findings table and api endpoint inventory are reviewed with you before build.
- 3
Build
Iterative delivery of severity labels, remediation status, risk summary with regular progress updates and demos.
- 4
Launch & support
Testing, deployment, handover documentation and optional ongoing maintenance.
With a similar project
- ✓Written scope and rules of engagement before any testing
- ✓Clear severity-rated findings with remediation steps
- ✓A readable executive summary for non-technical stakeholders
- ✓Retest guidance after fixes are applied
Security work is only performed on systems you own or have written permission to test. An assessment reduces risk; it cannot guarantee complete security.